Security
Where your clients’ data goes,and who can reach it
You hold confidential financial records under professional privilege. Before you put any of it into a tool, you are entitled to a straight answer about where it lives, who can see it, and what happens when you leave.
The first question a firm asks
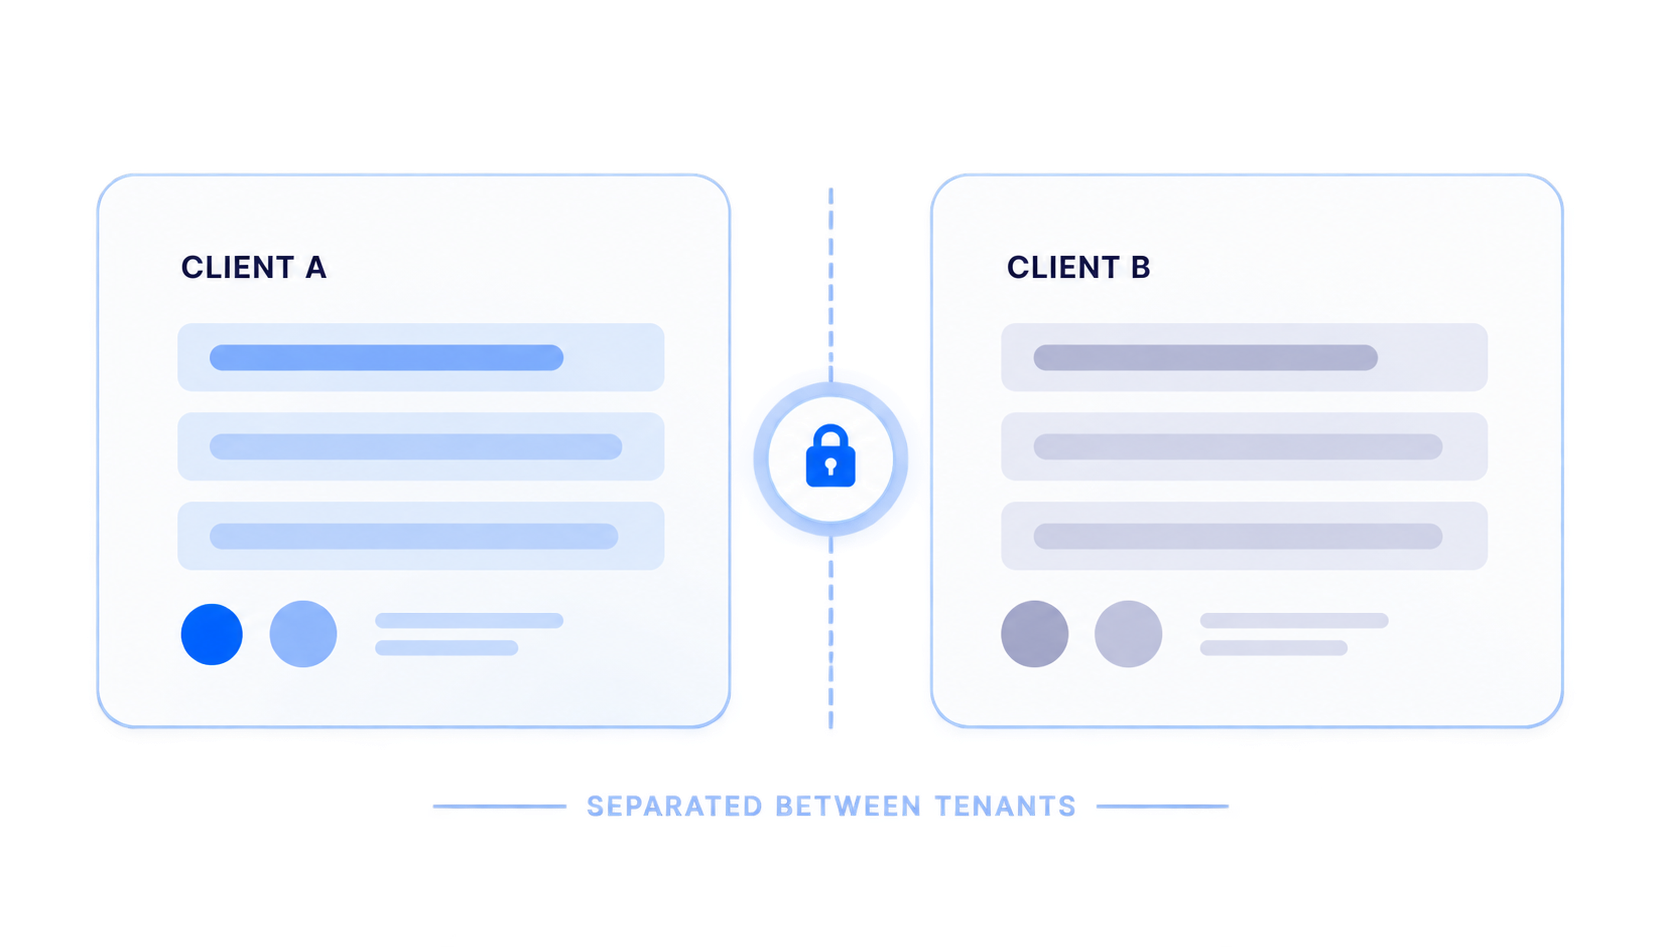
One client’s data is held apart from another’s.
Client data is separated between tenants, and role- and permission-level segregation inside a tenant controls what each person at your firm can reach. You are entitled to know exactly how far that goes before you ask, so we have set it out here rather than waiting to be asked.
In detail
The answers a security review asks for.
Everything a procurement team needs to score us, in one place.
- Encryption in transit
- TLS 1.3 with FIPS-validated ciphers
- Encryption at rest
- All client data encrypted at rest
- Tenant separation
- Client data is separated between tenants. Role- and permission-level segregation within a tenant is in development.
- Identity
- Microsoft Entra ID — multi-tenant, with external federation
- Access logs
- Working-paper access restricted and logged by role
- Administrative changes
- Every change recorded and visible in the app
- Backups
- Rollback and restoration from backup
- At close-out
- Authorised disposal of transitory data when the file closes
- Deployment
- Containerised, with rolling zero-downtime upgrades
- Availability
- Service-level and uptime reporting
- Hosting, sub-processors & certifications
- Set out in full in the security pack
Built on three commitments
Three commitments the product is built around.
These describe how Ordit is designed to behave. They are stated here as design intent and must be confirmed by Ordit before publication.
- 01
Client data is separated
Data belonging to one client is separated from another’s at the tenant boundary, and from another person at your own firm by role and permission.
- 02
Access follows the role
A person sees the engagements they were invited to and nothing else, with access following the role they already hold at your firm — mapped from Microsoft Entra ID rather than maintained twice.
- 03
Audit activity is recorded
Audit activity is tracked across the engagement, working-paper access is restricted and logged by role, and administrative changes are visible in the app.
Take the security pack to your review.
Architecture, hosting, sub-processors, certifications and policies — everything your committee will ask for.